Protecting Whistleblower Sources Online: Deploying SecureDrop Protocols in 6 Practical Steps
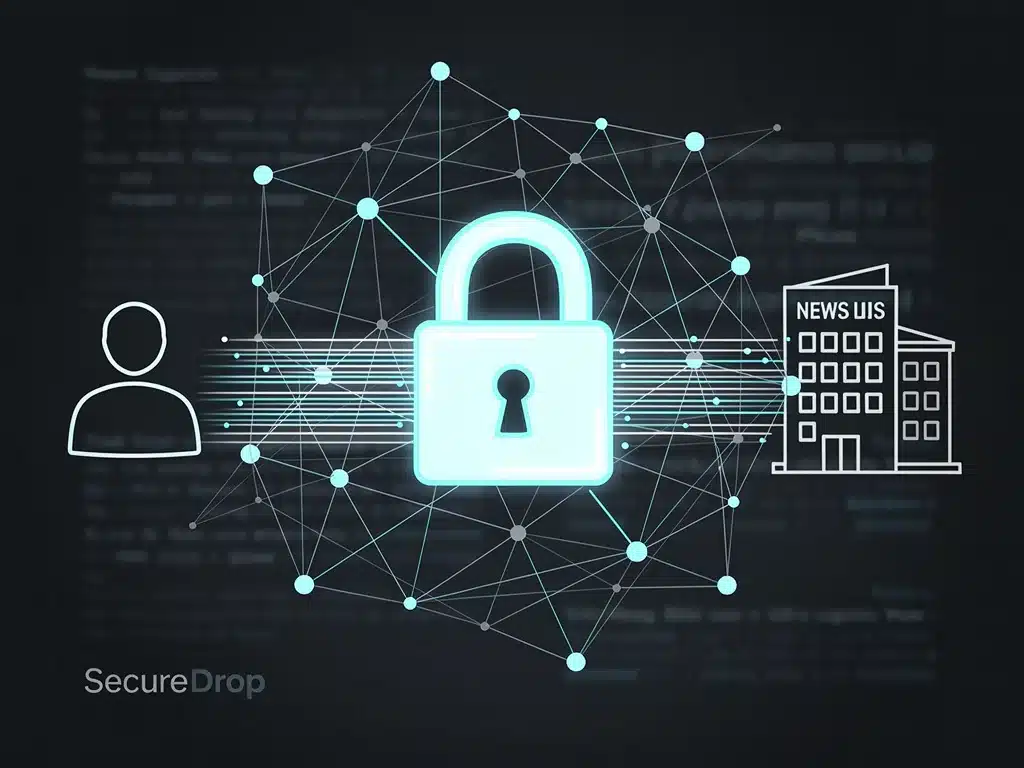
In an era of ubiquitous digital surveillance, mastering SecureDrop Protocols has become a vital imperative for newsrooms committed to safeguarding investigative informants.
Implementing these encrypted submission architectures ensures that sensitive leads reach journalists without leaving paper trails or digital footprints.
By combining Tor onion services, air-gapped decryption environments, and hardened open-source frameworks, modern media organizations can neutralize sophisticated tracking risks.
These technical safeguards create an impenetrable bridge between anonymous informants and investigative teams operating under intense legal scrutiny.
Whether you manage cybersecurity infrastructure or oversee investigative desks across the United States, understanding these operational security standards is essential.
Here is a practical six-step roadmap detailing recent developments, critical implementation requirements, and key security practices to monitor next.
The Imperative of Secure Communication for Whistleblowers
In an era where digital surveillance is pervasive, the need for robust mechanisms to protect confidential sources has never been more critical. Journalists and news organizations worldwide rely on whistleblowers to expose corruption, malfeasance, and critical truths that serve the public interest.
However, the risks associated with leaking sensitive information are substantial, often leading to severe repercussions for the source. This reality underscores the urgent demand for secure, anonymous communication channels that shield whistleblowers from identification and retaliation.
SecureDrop emerges as a paramount solution, offering a platform designed specifically to facilitate anonymous communication between whistleblowers and journalists. Its architecture is built upon principles of privacy and security, making it an indispensable tool for safeguarding sensitive disclosures.
Understanding SecureDrop: Architecture and Principles
SecureDrop is an open-source whistleblower submission system that allows individuals to anonymously share documents and messages with news organizations.
Developed by the Freedom of the Press Foundation, it leverages the Tor network to obscure IP addresses and encrypt communications, ensuring anonymity.
The system operates on a dedicated, air-gapped server controlled by the news organization, further enhancing its security posture. This isolation prevents external compromise and ensures that the integrity of the submissions remains intact, even in the face of sophisticated attacks.
At its core, SecureDrop embodies a commitment to journalistic integrity and the protection of sources, providing a critical infrastructure for investigative reporting. Its design is a testament to the ongoing battle against censorship and the right to information.
Core Components of SecureDrop
- Submission System: An online portal accessible via Tor, allowing whistleblowers to upload documents and send messages anonymously.
- Receiving System: An air-gapped computer used by journalists to access and decrypt submissions, ensuring it never connects to the internet directly.
- Operational Security: Strict protocols for handling submissions, including physical security of servers and regular audits to maintain system integrity.
Step-by-Step Guide to Deploying SecureDrop Protocols
Deploying SecureDrop is a methodical process that requires careful planning and execution to ensure maximum security and functionality. News organizations must commit resources and expertise to establish a secure and reliable instance of the system.
This deployment involves several critical stages, from initial hardware setup to ongoing maintenance and training. Each step is vital in establishing a robust framework for SecureDrop Protocols.
Adherence to these protocols is not merely technical; it is a fundamental commitment to ethical journalism and the protection of those who bravely come forward with sensitive information. Proper implementation minimises vulnerabilities and builds trust with potential sources.
Step 1: Hardware Acquisition and Preparation
The first critical step involves acquiring the necessary hardware for your SecureDrop instance. This typically includes at least two dedicated servers: one for the web/application server and another for the monitor server.
Additionally, an air-gapped journalist workstation is essential for secure access to submissions.
All hardware should be new, securely sourced, and dedicated solely to SecureDrop operations to minimise potential vulnerabilities.
Physical security of these machines is paramount, requiring them to be housed in a secure, access-controlled environment within the news organization’s premises.
Proper preparation also includes installing a minimal operating system, typically a hardened version of Debian or Ubuntu, and ensuring all firmware is up to date. This foundational security prevents supply chain attacks and establishes a clean environment for deployment.
Step 2: Network Configuration and Tor Integration
Network configuration is a complex but crucial aspect of SecureDrop deployment. The web server must be configured to operate as a Tor hidden service, allowing whistleblowers to submit information anonymously without revealing the news organization’s IP address.
This involves setting up appropriate firewall rules to restrict access and ensure only necessary ports are open.
Careful attention to network segmentation is also vital, separating the SecureDrop infrastructure from the news organization’s main network to prevent cross-contamination in case of a breach.
Integrating Tor correctly ensures that all communications to and from the whistleblower interface are routed through the Tor network, providing robust anonymity. This step is fundamental to SecureDrop Protocols effectively.
- Tor Hidden Service Setup: Configure the web server to run as a Tor hidden service, generating a unique .onion address.
- Firewall Rules: Implement strict firewall rules to isolate the SecureDrop server and allow only necessary traffic.
- Network Segmentation: Ensure the SecureDrop network is physically and logically separate from the main organizational network.
Step 3: Installation of SecureDrop Software
With the hardware and network foundation established, the next step is the installation of the SecureDrop software itself. This process is typically guided by detailed documentation provided by the Freedom of the Press Foundation, which outlines specific commands and configurations.
The installation involves setting up the various components, including the web application, the admin interface, and the monitoring tools. It is crucial to follow the instructions meticulously to avoid misconfigurations that could compromise the system’s security.
Regularly checking for updates and applying patches immediately is also part of maintaining a secure installation. This proactive approach is essential for SecureDrop Protocols against emerging threats.
Step 4: Hardening the System and Operational Security
System hardening goes beyond basic installation, involving a series of measures to reduce the attack surface and enhance the overall security posture. This includes disabling unnecessary services, implementing strong password policies, and configuring intrusion detection systems.
Operational security, or OpSec, extends to the human element. Journalists and administrators accessing the SecureDrop system must adhere to strict protocols, such as using strong, unique passphrases, multi-factor authentication, and operating the air-gapped workstation in a secure manner.
Training staff on these protocols is paramount, as human error remains a significant vulnerability. Continuous education and drills ensure that all personnel understand their role in SecureDrop Protocols.
- Disable Unnecessary Services: Minimise the software footprint to reduce potential attack vectors.
- Strong Authentication: Enforce multi-factor authentication and complex passphrases for all access points.
- Regular Security Audits: Conduct frequent internal and external security audits to identify and rectify vulnerabilities.
Step 5: Journalist Workstation Setup and Usage
The journalist workstation is the interface through which submissions are accessed and processed. Crucially, this machine must be air-gapped, meaning it never connects to the internet or any other network, thus preventing any potential malware or surveillance from reaching the sensitive data.
This workstation is typically a dedicated computer running a secure operating system like Tails, which routes all internet traffic through Tor and leaves no trace on shutdown. Journalists use this machine to decrypt submissions, review documents, and communicate with sources.
Strict protocols govern the use of the journalist workstation, including physical security, regular wiping, and adherence to specific workflows for handling sensitive information. This meticulous approach is central to SecureDrop Protocols.
Step 6: Ongoing Maintenance and Training
Deployment is not a one-time event; SecureDrop requires continuous maintenance and regular updates to remain secure and effective. This includes applying software patches, updating the operating system, and monitoring system logs for any suspicious activity.
Regular training for journalists and technical staff is also essential. As digital threats evolve, so too must the understanding and practices of those operating the system. Training should cover threat models, new vulnerabilities, and best practices for secure communication.
A commitment to ongoing vigilance and adaptation is key to the long-term success of SecureDrop. This ensures that the system continues to provide a safe haven for whistleblowers and a reliable channel for critical information, reinforcing the mission of SecureDrop Protocols.
Why Continuous Vigilance is Critical
The landscape of digital security is constantly changing, with new threats and vulnerabilities emerging regularly. Therefore, a static approach to security is inherently insufficient, especially when dealing with sensitive information from whistleblowers.
Continuous vigilance involves proactive monitoring, regular security audits, and staying informed about the latest cyber security developments. This ensures that any potential weaknesses in the SecureDrop system are identified and addressed promptly, before they can be exploited.
This commitment to ongoing security is not just a technical requirement; it is an ethical imperative for news organizations. It builds and maintains the trust of whistleblowers, who rely on these systems for their safety and anonymity, directly impacting the ability to conduct impactful investigative journalism.
| Key Aspect | Brief Description |
|---|---|
| Source Anonymity | SecureDrop uses Tor to protect whistleblower identities and locations. |
| System Isolation | Air-gapped servers and workstations prevent internet exposure. |
| Operational Protocols | Strict guidelines for staff handling sensitive whistleblower submissions. |
| Continuous Updates | Regular software patches and security audits are essential for system integrity. |
Frequently Asked Questions About SecureDrop Deployment
SecureDrop is an open-source platform facilitating anonymous communication between whistleblowers and journalists. It is crucial for protecting sources who expose critical information, ensuring their anonymity and safety from retaliation. Its importance lies in enabling investigative journalism that often relies on confidential disclosures.
SecureDrop uses the Tor network to obscure the whistleblower’s IP address and encrypt all communications. Submissions are processed on an air-gapped system, preventing any direct internet connection. This multi-layered approach makes it extremely difficult to trace the source, ensuring robust anonymity.
Key hardware includes two dedicated servers (web/application and monitor) and an air-gapped journalist workstation. All hardware must be new, securely sourced, and used exclusively for SecureDrop. Physical security of these machines is also a critical requirement.
Absolutely. Comprehensive training for journalists and technical staff is paramount. This covers operational security protocols, threat models, and best practices for handling sensitive information. Human error is a significant vulnerability, so continuous education ensures system integrity and source protection.
Ongoing maintenance, including regular software updates, security patches, and system monitoring, is vital. The digital threat landscape evolves constantly, so continuous vigilance ensures the system remains secure against new vulnerabilities. This proactive approach sustains the integrity of Protecting Whistleblower Sources Online: Deploying SecureDrop Protocols in 6 Practical Steps.
Looking Ahead: The Future of Source Protection
The successful deployment and diligent maintenance of SecureDrop protocols represent a significant stride in safeguarding journalistic sources.
As digital threats continue to escalate, the adoption of such advanced security measures will become increasingly commonplace, not just for large news organizations but for smaller independent outlets as well.
The continuous evolution of SecureDrop and similar tools will be critical in adapting to new surveillance technologies and cyber-attack methodologies.
This ongoing arms race between those seeking to expose truth and those seeking to suppress it underscores the necessity of robust, adaptable security frameworks.
Ultimately, the commitment to SecureDrop Protocols is a commitment to the very foundation of a free press and an informed public. It ensures that vital information can reach the public sphere, even when powerful entities wish to keep it hidden, fostering transparency and accountability.